Chainguard-Workspaces
Geben Sie Ihren Agenten Raum zum Arbeiten, nicht zum Streunen
Ermöglichen Sie eine schnellere agentenbasierte Entwicklung – abgesichert durch die gehärtete Isolation, die Unternehmenssicherheit erfordert.
Isolieren Sie nicht vertrauenswürdigen Code in durch Chainguard gehärteten MicroVMs, damit bösartige Agenten Ihre Systeme nicht kompromittieren oder Ihre Geheimnisse stehlen können.
Environments start in seconds with pre-loaded dependencies, so developers and agents can jump straight to work.
WHY CHAINGUARD?
Agent isolation, built differently
Layers of defense
Workspace microVMs are built with Chainguard OS Packages, including FIPS-compliant toolchains. Dependencies are verified against your lockfile as it runs, preventing untrusted code from executing.
Exfiltration-safe by design
Real credentials stay outside the workspace. Tools needing credentials on disk get short-lived, encrypted stand-ins that are useless if stolen.
Fast starts and resumes
Workspaces launch and resume in seconds from warm snapshots, seamlessly restoring your working tree, uncommitted edits, shell, and background processes.
Full visibility
Every run generates a tamper-proof record of your environment, commands, code changes, and network calls.
Workspace rollback
Run agent loops risk-free. Pre-execution state snapshots let you quickly revert package changes, configs, and untracked files without affecting other workspaces.
Stop agents from guessing
Route agent questions to developers. Workspaces are snapshotted and paused after 10 minutes, halting compute spend until answered.
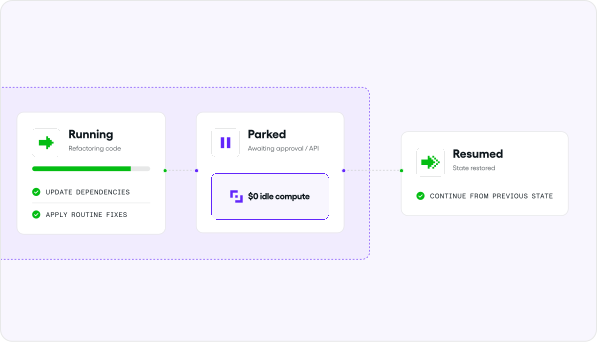
Autonomous code maintenance and refactoring
Execute background agents that refactor legacy codebases, update outdated dependencies, and apply routine code fixes across repositories without risking broad network access or standing production secrets. Gracefully pause execution while awaiting human approval or external API responses, parking the sandbox at no cost until the agent is unblocked, and then resume from its previous state.
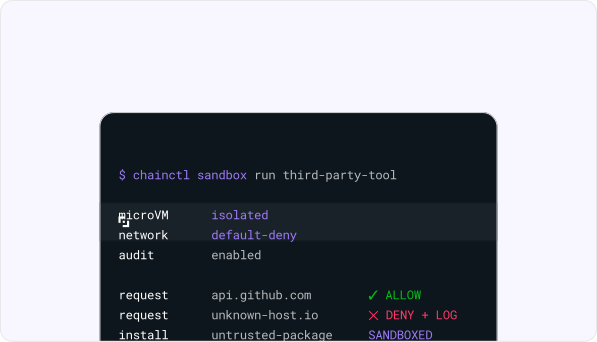
Untrusted tool and third-party skill execution
Safely run arbitrary agent scripts, untrusted package installs, and third-party Model Context Protocol (MCP) integrations inside microVMs with configurable default-deny policies that block unsanctioned outbound network traffic and log all agent actions for security and compliance review.
Gated pull request generation
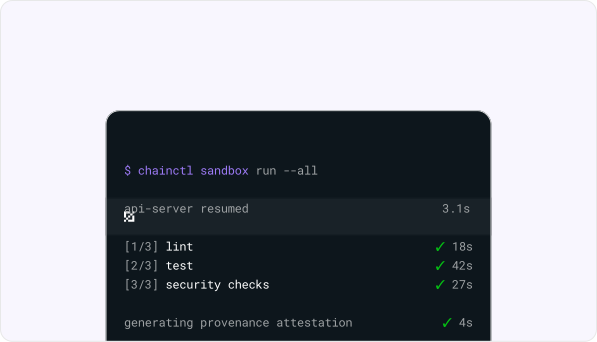
Call Chainguard Checks on agent-generated code and attach cryptographic proof to ensure incoming changes are fully pre-tested and verified, so every PR is born green.
Trust in every phase of the SDLC
Explore the rest of Chainguard's product suite
Code safely with agents
Build with trusted artifacts
Ship through trusted CI
Chainguard Workspaces is currently in beta and is a Technology Preview under Chainguard's Master Services and License Agreement.